Q3 2026: Higher Education Got Hammered
Every quarter I dig through the MILBERT identity data from our customers. Q3 just wrapped. Higher education got hammered.
How to read the chart: rates are accounts affected per 1,000 accounts per month, so different sized environments compare cleanly. Categories overlap. Do not add them together. These are detections of what hit the environment, not confirmed compromises, and not a count of what got through.
MILBERT is agentic AI. When it sees bad activity on an account, it takes the first action to stop the actor: kill the session, revoke tokens, reset MFA, or block the identity while the attempt is still in play. A high bar means more accounts saw that activity. It does not mean the activity won.
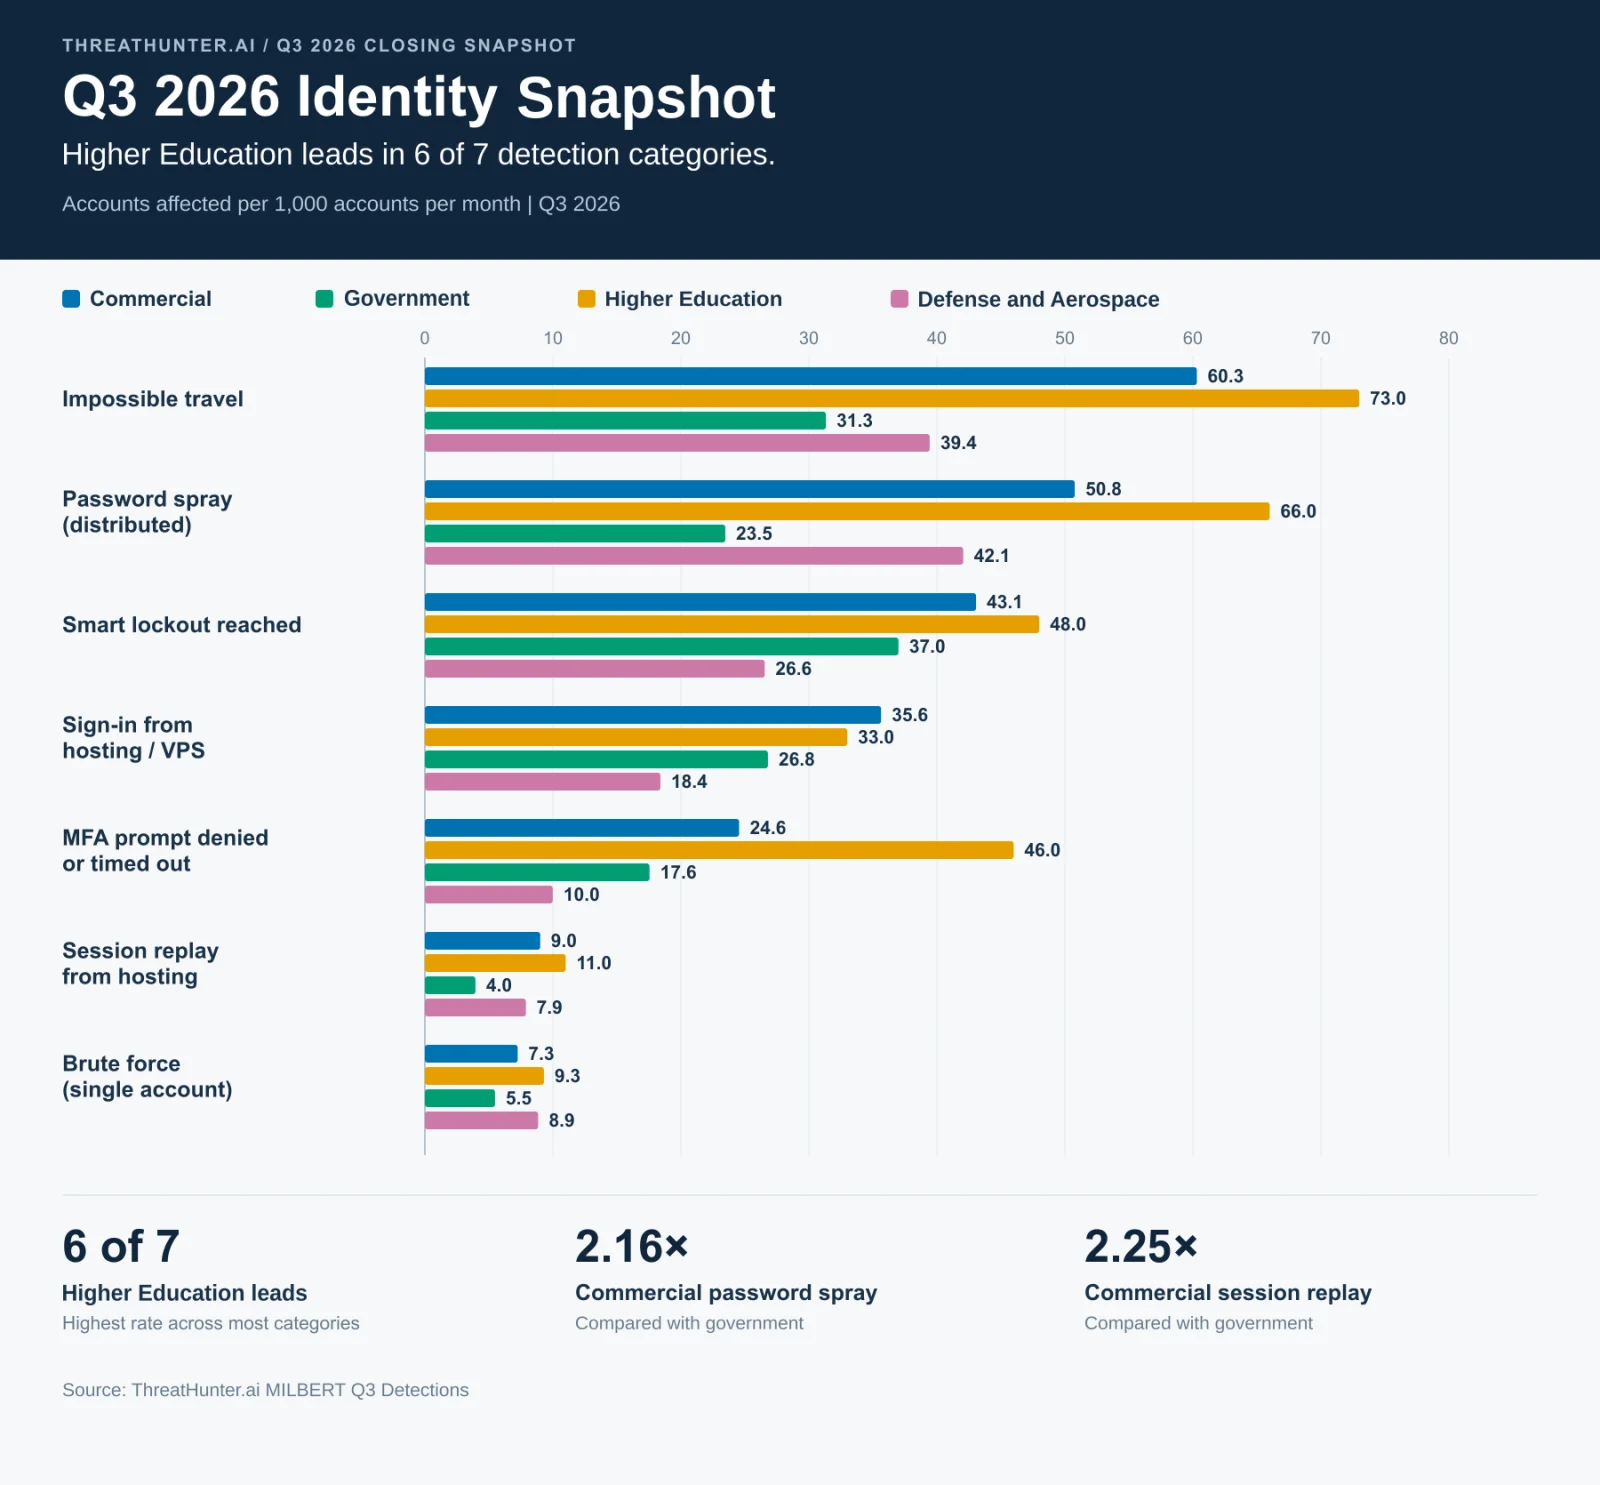
Source: ThreatHunter.ai MILBERT Q3 2026 detections.
Higher education took the beating
Higher education led six of the seven categories. Impossible travel hit 73 accounts per 1,000. Distributed password spray hit 66. Smart lockout hit 48. MFA prompts denied or timed out hit 46. Session replay from hosting was highest here too, at 11 per 1,000.
That MFA number deserves a closer look. Almost 5% of higher education accounts saw an MFA prompt that nobody approved. Some of that is clumsy phones. All of it is worth investigating.
Commercial owns the VPS problem
Commercial is a wide bucket. It covers healthcare, financial services, manufacturing, energy and utilities, retail and e-commerce, hospitality and entertainment, transportation and logistics, technology and telecom, professional services, construction and real estate, life sciences, agriculture, and media. The commercial rate is an average across very different shops.
The one category higher education did not lead was sign-ins from hosting and VPS infrastructure. Commercial led at 35.6 per 1,000, ahead of higher education at 33. Real users rarely sign in to email from a rented server.
Commercial also ran more than double government on password spray (50.8 vs 23.5) and on session replay from hosting (9.0 vs 4.0). Session replay is the one that matters most. That is a session that already cleared MFA, reused from somewhere else. MFA did its job, and it still was not enough.
Defense, aerospace, and government
Defense and aerospace is mixed. Password spray landed at 42.1, third highest. Brute force hit 8.9, just behind higher education at 9.3. At the same time, they posted the lowest rates on smart lockout, VPS sign-ins, and MFA denials. Plenty of knocking, fewer of the signals that usually follow. I am watching that pattern.
Government came in lowest on four of the seven: impossible travel, password spray, session replay, and brute force. Do not read that as safe. A low rate does not mean a clean environment, and it does not mean you are seeing everything. Sometimes attackers really did go elsewhere. Sometimes the picture is limited visibility: logs that are not flowing, integrations that are not on, licensing that does not expose the signals you need. On a chart, that looks like good news. Same warning applies to the quiet defense and aerospace bars. If the numbers look quiet, the first question is whether you can see.
Q3 makes the post-login gap hard to argue with. Spray, MFA pressure, VPS sign-ins, and session replay showed up in the same customer set. Password and MFA are not the finish line. That gap is where we built MILBERT to sit. If these rates look like yours, or yours look a little too quiet, reach out. I am happy to walk through it.